Penetration Testing
Learn the structured, ethical methodology of offensive security testing. Master network enumeration, web vulnerability exploitation, privilege escalation, and remediation reporting.
🛠️ Industry Tools Mastered
Nmap · Burp Suite · Metasploit · Kali Linux
🎯 Target Career Roles
Direct qualification for Enterprise SOC, Threat Hunting, GRC Auditing, PenTesting & Blue/Red Teams.
📜 Included with Enrollment
12 Comprehensive Modules (6 Hands-on Lab Modules + 6 Deep Illustrative Case Modules), Verified Standard Guides, Capstone Review & Verifiable Certificate.
Comprehensive 12-Module Curriculum
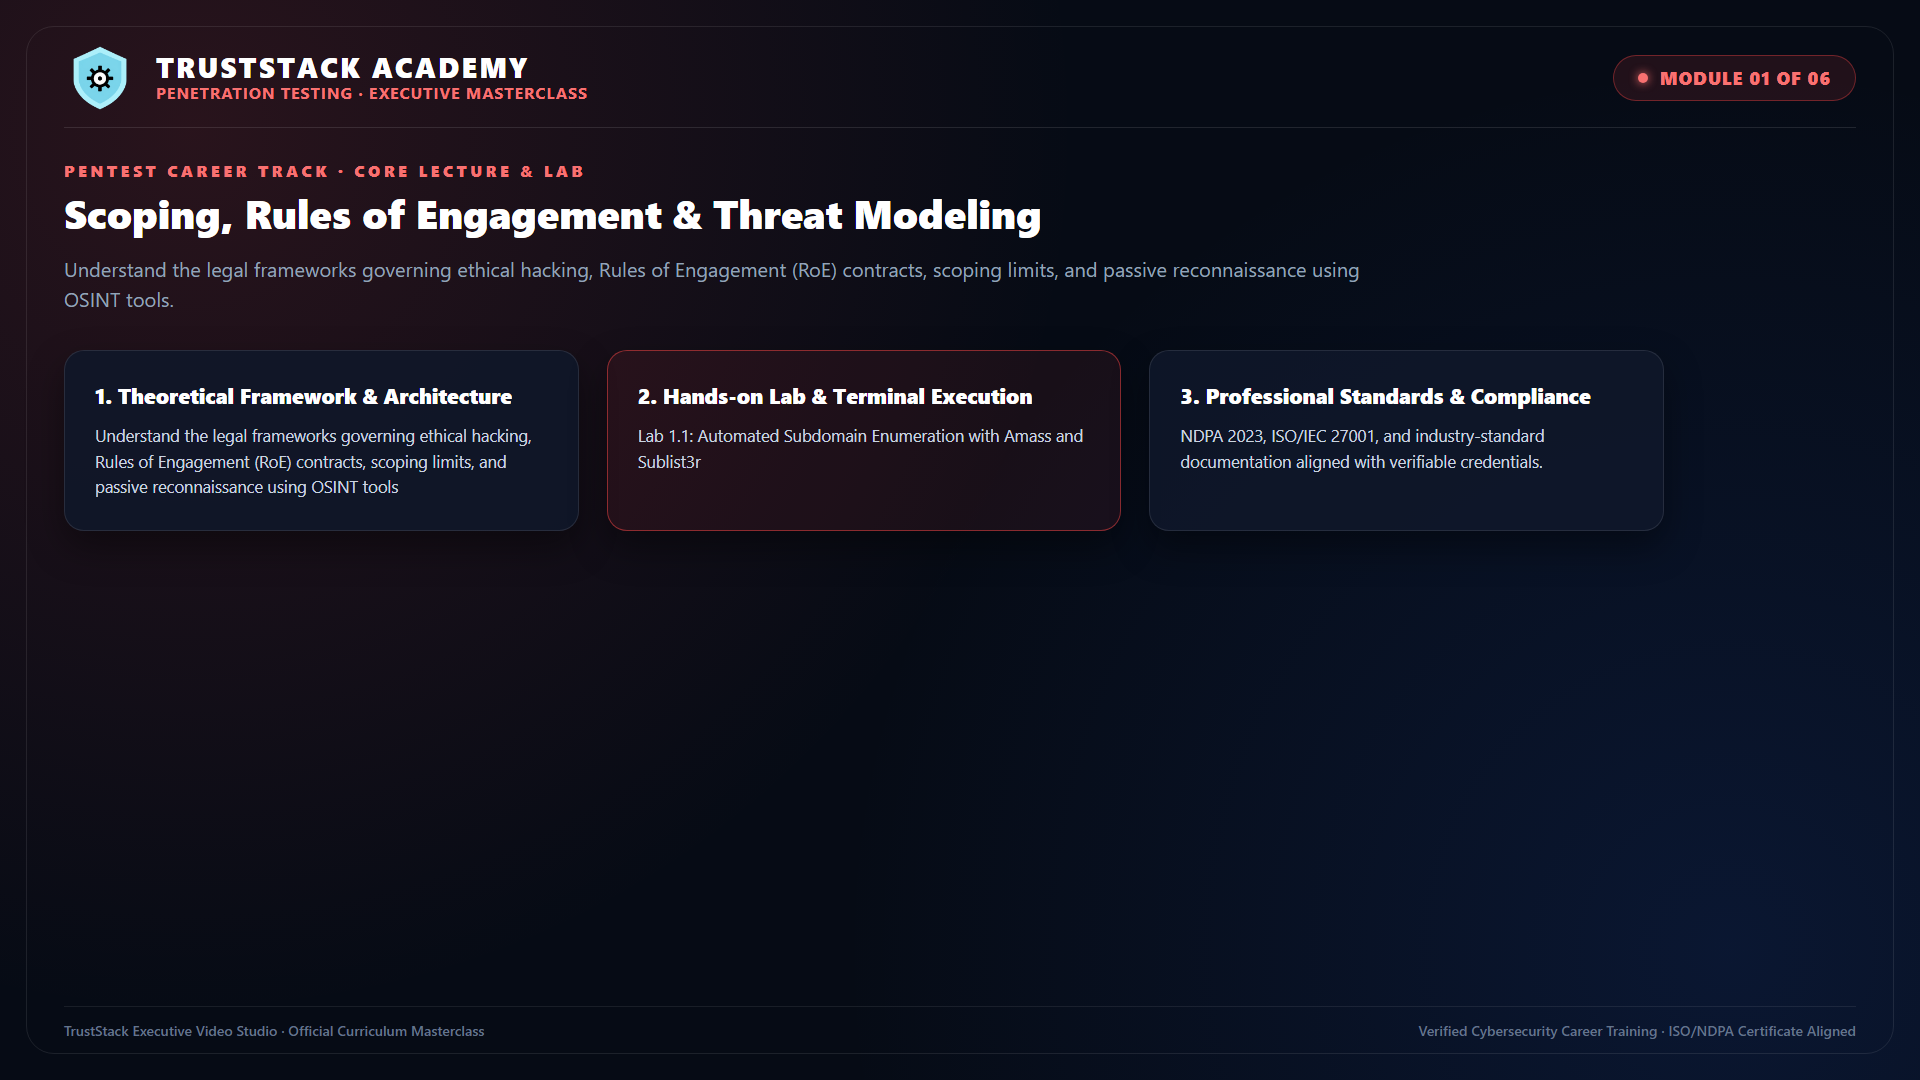
Inspect the complete course structure across all 12 modules. Modules 01 through 06 combine core lectures with 12 hands-on cloud labs; Modules 07 through 12 deliver advanced illustrative study, real-world case scenarios, architectural frameworks, and expert insights with zero lab dependencies.
Real-World Industry Portfolio Project
Every student completes an exhaustive, multi-stage capstone scenario mirroring enterprise incidents in African and global banking, telecom, and critical infrastructure environments.
- ✓ Professional incident report or audit dossier ready for employers
- ✓ Live defense presentation and technical oral review
- ✓ Verifiable cryptographic credential registered on TrustStack Registry
Discover More Career Tracks
TrustStack Academy equips you across all defensive, offensive, and governance domains.
SOC Analyst Track
Build the practical skills to monitor security events, investigate alerts, hunt threa...
View Track Structure →Digital Forensics
Preserve evidence, reconstruct attacks, detect anti-forensics, and produce defensible...
View Track Structure →Threat Intelligence
Turn threat data into actionable intelligence using structured analysis, adversary tr...
View Track Structure →Cloud Security
Secure cloud identities, workloads, data, and infrastructure across AWS and Azure usi...
View Track Structure →Governance & GRC
Translate security and privacy obligations into practical policies, risks, controls, ...
View Track Structure →Malware Analysis
Safely examine suspicious files, unpack obfuscated binaries, analyze in-memory proces...
View Track Structure →Security Engineering
Design and build secure systems by applying Zero Trust architecture, DevSecOps automa...
View Track Structure →ISO/IEC 27001 Lead Implementer
Master Information Security Management Systems (ISMS), Clauses 4–10 implementation, I...
View Track Structure →Cybersecurity for Managers & Executives
Boardroom Cyber Risk Governance, Delaware Caremark Fiduciary Compliance, FAIR™ Quanti...
View Track Structure →Business Continuity Planning (BCP) & Disaster Recovery Planning (DRP)
Enterprise Resilience Blueprint: ISO 22301 Lifecycle, Business Impact Analysis (BIA) ...
View Track Structure →